
You’ve likely seen strange redirects or pop-ups and unknown admin accounts and tried scanning your site for malware. But getting rid of obvious, infected files might not be enough to get rid of backdoors hackers can use to come back.
In this guide, you’ll discover how to clean a hacked WordPress website step-by-step, how to check that your site is clean, and how to avoid infection again.
Key Takeaways
- WordPress malware can inject malicious code, spam links, redirects, and unauthorized administrator accounts.
- Malware cleanup requires inspecting website files, databases, plugins, themes, and user accounts.
- Backdoors can allow attackers to regain access even after visible malware disappears.
- Security scanners help identify threats but do not guarantee complete malware removal.
- Google Search Console helps identify security warnings affecting website visitors and search visibility.
- Regular updates, strong passwords, and backups reduce future security risks.
What Is a Hacked WordPress Website?
A hacked WordPress website is a website accessed or modified without authorization, often resulting in malicious code, suspicious administrator accounts, injected content, or unwanted redirects.
Moreover, WordPress malware can enter through outdated plugins, vulnerable themes, stolen passwords, or insecure hosting accounts.
Common WordPress attacks include:
- Malware and malicious PHP file injections.
- SEO spam pages and unauthorized backlinks.
- Phishing pages and suspicious redirects.
- Hidden administrator accounts and backdoors.
- Unauthorized JavaScript injections.
For example, a business website may suddenly redirect mobile visitors to an unrelated gambling or phishing website.
Why Is Cleaning a Hacked WordPress Site Important?
WordPress malware cleanup is important because an infected website can put visitors at risk hurt search engine rankings and stop business activities. For example Google Safe Browsing might show a warning that says the site is dangerous if it has content. If the infection is not fixed several serious issues can happen.
- Visitor security risks: Malicious scripts can trick visitors into giving away information or downloading harmful files.
- SEO problems: Spam pages and hidden links added by malware can lower the website’s visibility, in search results.
- Hosting suspension: Hosting companies may block or disable websites that are infected.
- Reputation damage: Visitors may lose trust in the website. Avoid it in the future.
- Downtime: The time needed to clean the site can mean lost messages, inquiries and sales.
How Can You Tell If Your WordPress Website Has Malware?
WordPress malware detection involves checking unusual website behaviour, suspicious files, unauthorized accounts, and security notifications.
Watch for these warning signs:
- Unexpected redirects to unfamiliar domains.
- Unknown WordPress administrator accounts.
- Unfamiliar PHP files or modified core files.
- Unexpected pop-ups and spam pages.
- Unusual server resource consumption.
- Google Search Console security warnings.
For example, open Google Search Console and check Security Issues under the Security and Manual Actions section.
How Do You Clean a Hacked WordPress Site Step by Step?
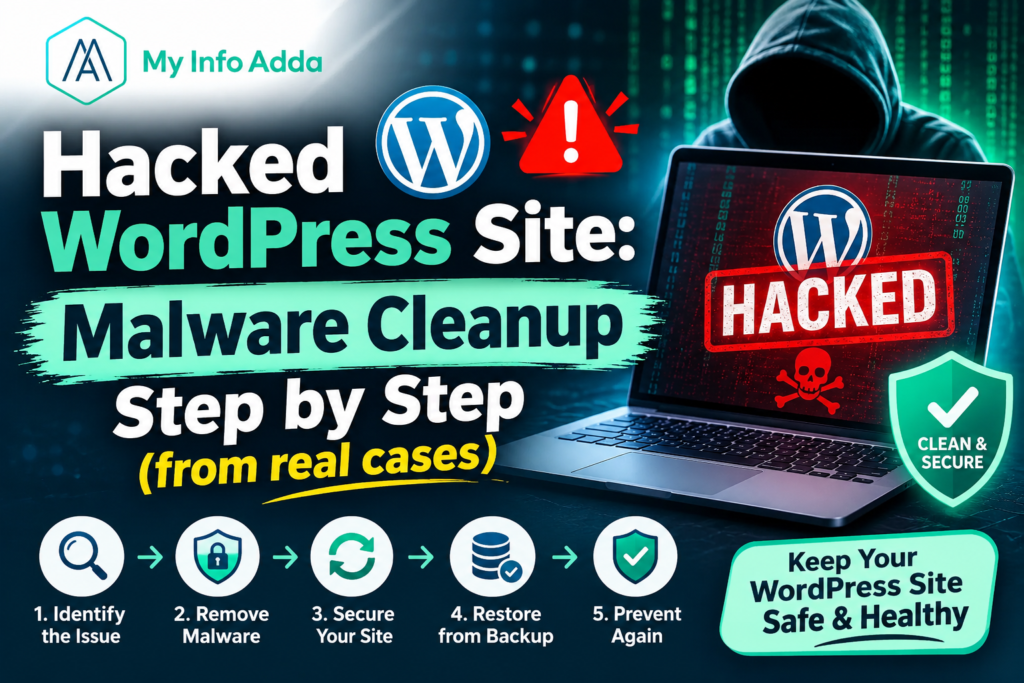
WordPress malware cleanup involves identifying infected files, removing malicious code, replacing compromised software, checking database changes, and securing the accounts and systems that allowed the attack.
Follow this recovery process:
- Restrict website access: Enable maintenance mode if necessary to reduce visitor exposure.
- Back up infected files: Save copies of website files and the database for investigation. Never assume this backup is safe to restore.
- Contact your hosting provider: Request malware reports, server logs, and assistance identifying compromised files.
- Scan for malware: Use reputable scanners to identify suspicious files and injected code.
- Change passwords: Update WordPress, hosting, FTP/SFTP, database, and other affected credentials. Revoke suspicious sessions and API keys.
- Replace infected software: Reinstall WordPress core files, plugins, and themes using trusted, clean versions.
- Inspect the database: Check administrator accounts, injected links, spam content, and unexpected changes.
- Find hidden backdoors: Investigate suspicious PHP files, configuration changes, and unauthorized scheduled tasks.
- Update everything: Install patched WordPress, plugin, and theme versions. Remove unused extensions.
- Test your website: Check login access, forms, redirects, important pages, and website functionality.
Important: Never delete unfamiliar files without checking their purpose. Some legitimate WordPress files may look suspicious to beginners.
How Do You Remove Malicious Redirects from WordPress?
Malicious WordPress redirects occur when attackers inject unauthorized code into website files, plugins, themes, database records, or server configuration files to send visitors to unwanted destinations.
For example, your homepage may work normally on desktop but redirect mobile visitors to a suspicious shopping website.
Check these locations:
- .htaccess for unauthorized redirect rules.
- Theme files such as functions.php and header.php.
- Plugin files containing suspicious scripts.
- Database records containing injected links or JavaScript.
After removing the infection, clear WordPress, browser, hosting, and CDN caches. Test the website using different browsers and devices.
Which WordPress Malware Removal Tools Should You Use?
WordPress security tools help detect suspicious activity, scan files, and protect websites against common attacks.
| Tool | Main purpose |
| Wordfence | Firewall, malware scanning, file integrity checks |
| Sucuri SiteCheck | External website malware scanning |
| MalCare | Malware detection and cleanup features |
| Google Search Console | Security warnings and search monitoring |
| Hosting scanner | Server-level malware investigation |
Does Wordfence automatically remove malware from WordPress?
Wordfence helps detect WordPress malware through file scanning and security monitoring. I notice that automatic repair or deletion depends on the infected file and on the repair options that are available.
The Wordfence repair feature can replace modified core or repository files with clean versions. Wordfence deletion options can remove identified files but I also see that custom code and hidden backdoors may require manual investigation.
How Do You Check If Your WordPress Website Is Completely Clean?
A WordPress website should be considered recovered after malware scans, file checks, database inspections, redirect tests and account security reviews show no remaining signs of compromise.
Use this verification checklist:
- Run another malware scan.
- Check all administrator accounts.
- Review file modifications.
- Inspect database entries.
- Test website redirects on mobile and desktop.
- Check Google Search Console Security Issues.
- Test forms, login pages and important functionality.
Request a Google review after resolving reported security problems.
Remember: One clean scan does not guarantee that every hidden backdoor has been removed.
How Can You Protect Your WordPress Website from Future Hackers?
Keeping a WordPress website safe from hackers means doing software updates using strong passwords using two-factor authentication installing only trusted plugins keeping secure backups and watching the site for security problems.
Follow these precautions:
- Keep WordPress, plugins and themes updated.
- Use passwords and two-factor authentication.
- Install. Themes only, from trusted sources.
- Remove extensions that’re unused or abandoned.
- Enable a web application firewall.
- Schedule automated. Test restoring them.
- Use hosting and SFTP.
- Apply file permissions.
- Monitor administrator accounts and website files.
What’s Next? Your WordPress Security Recovery Checklist
A successful recovery requires more than deleting suspicious files. Before considering your website secure, complete these final actions:
- Remove malicious code and infected files.
- Secure all affected accounts.
- Replace compromised software.
- Update WordPress and extensions.
- Check database changes and hidden backdoors.
- Verify redirects and website functionality.
- Perform a comprehensive malware scan of the website.
- Check Google Search Console for any new website alerts or messages.
- Configure regular backups and security monitoring.
Conclusion: Keep Your WordPress Website Clean and Secure
Cleaning a hacked WordPress site requires finding the entry point getting rid of code making sure stolen accounts are safe and looking for secret ways in.
Also keeping things up, to date having backups that work and watching for problems can help prevent more issues. Don’t trust one check for malware to say your site is okay. Make sure everything is fixed and keep an eye on your site.
Frequently Asked Questions About Cleaning a Hacked WordPress Site
1. How do I clean a hacked WordPress site?
To clean a hacked WordPress site, back up infected files, scan for malware, identify suspicious code, replace compromised plugins and themes, inspect the database, and remove hidden backdoors. Finally, change passwords, update WordPress, and run another security scan.
2. How do I know if my WordPress website has malware?
Common signs of WordPress malware include unexpected redirects, suspicious pop-ups, unknown administrator accounts, unfamiliar PHP files, injected spam links, and unusual server activity. You can also check Google Search Console’s Security Issues report.
3. Can I remove WordPress malware without deleting my website?
Yes, you can often remove WordPress malware without deleting your website content. Replace infected software with clean copies, remove malicious code, and carefully inspect the database while preserving legitimate posts, pages, images, and settings.
4. Does Wordfence automatically remove malware from WordPress?
Wordfence can identify malware and offer repair or deletion options for certain infected files. However, not every infection can be fixed automatically. Hidden backdoors, custom code injections, and database infections may require manual cleanup.
5. How do I remove malicious redirects from WordPress?
Check your .htaccess file, theme files, plugins, database records, and injected JavaScript for unauthorized redirect code. Remove verified malicious code, clear website and CDN caches, and test redirects across different browsers and devices.